
Imagine your crypto exchange is ready to launch, but a single regulatory letter stops everything. That’s the reality for many digital asset businesses in 2026. Crypto compliance programs are no longer optional checkboxes; they are the operational backbone that allows legitimate businesses to survive and scale. With the EU's MiCA fully enforceable and the US navigating a complex patchwork of federal and state laws, the cost of getting it wrong is higher than ever. This guide breaks down what these programs actually look like in practice, how much they cost, and how you can build one without breaking the bank or user experience.
The Core Pillars of Modern Crypto Compliance
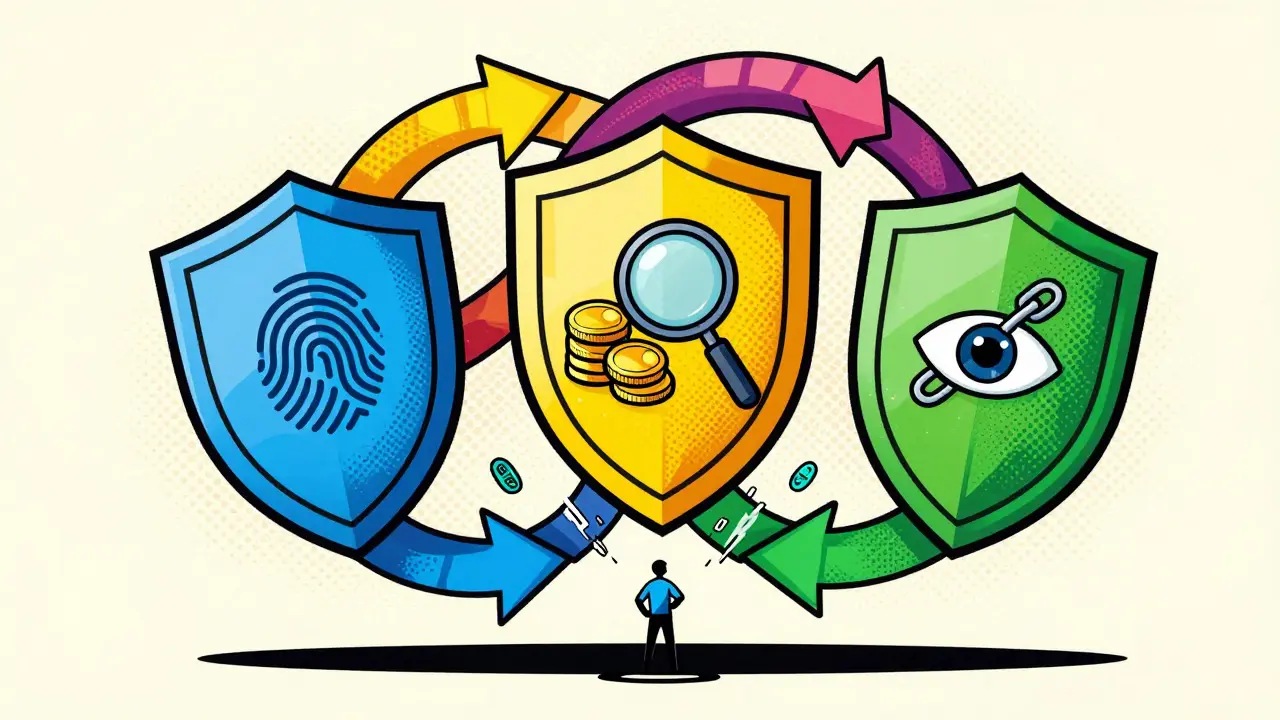
A robust compliance framework isn't just about checking boxes. It’s a dynamic system built on three interconnected pillars. First, you have Identity Verification (KYC), which confirms who your users are. Second, there is AML/PEP Screening, which checks if those users are involved in money laundering or are politically exposed persons. Finally, you need Wallet & Transaction Monitoring, which tracks funds as they move across the blockchain. These three elements work together to create a risk-based approach. For example, a user sending $50 might only need email verification, while someone moving $10,000 triggers Enhanced Due Diligence (EDD) requiring proof of wealth. This tiered system keeps friction low for small transactions while tightening security where the risk is highest.
Navigating the Global Regulatory Maze
The biggest headache for crypto companies is that there is no single global rulebook. The United States uses a fragmented approach involving multiple bodies like FinCEN, the SEC, and CFTC, plus state-level regulators. In fact, operating nationwide in the US can require up to 47 different state money transmitter licenses. In contrast, the European Union offers a unified path through MiCA (Markets in Crypto-Assets). MiCA provides a single license for pan-European operations, though it comes with strict capital requirements of €125,000 minimum for VASP registration. The UAE has also emerged as a major hub, with Dubai's VARA requiring specific three-tier KYC processes and an 8-year record retention period in ADGM/DIFC. Understanding these differences is critical because a strategy that works in London might fail in New York or Dubai.
| Jurisdiction | Key Regulation | Licensing Complexity | Record Retention | Estimated Cost Impact |
|---|---|---|---|---|
| United States | BSA / FinCEN Rules | High (Multi-state) | 5 Years | 37% Higher than EU |
| European Union | MiCA | Medium (Unified) | 5 Years | Baseline |
| UAE (Dubai) | VARA | Low-Medium (Fast Track) | 5-8 Years | Variable |
Technology Stack: Tools You Actually Need
You don’t have to build everything from scratch. Most successful firms rely on a tech stack that integrates identity providers like Sumsub, Onfido, or Veriff via API. These tools handle the heavy lifting of document scanning and biometric matching. But identity is only half the battle. You also need AI-powered transaction monitoring systems capable of processing thousands of transactions per second. Recent benchmarks show that modern systems can flag suspicious activities with over 98% accuracy, significantly reducing false positives compared to older rule-based methods. If you’re dealing with cross-border transfers, you must also comply with the Crypto Travel Rule, which mandates sharing sender and recipient information between Virtual Asset Service Providers (VASPs) for transactions exceeding $3,000. Integrating this seamlessly into your backend is often the most technically challenging part of the build.
Costs, Timelines, and Hidden Pitfalls
Let’s talk numbers. For a mid-sized exchange, expect to spend between $50,000 and $500,000 annually on comprehensive compliance solutions. Enterprise platforms can easily exceed $1 million per year. Beyond software, consulting fees add up fast. One EU exchange reported spending $350,000 just in consulting fees to implement MiCA compliance, plus $120,000 for annual maintenance. Time is another factor. Implementing a full program typically takes 6 to 9 months for mid-sized firms, stretching to 12-18 months for larger, more complex platforms. A common pitfall is ignoring the human element. Only 12% of traditional compliance professionals currently possess the specific skill set needed for blockchain. Hiring or training staff who understand both financial regulations and distributed ledger technology is non-negotiable. Without this expertise, your software will generate alerts that nobody knows how to interpret correctly.
Building Trust with Institutional Investors
Why go through all this trouble? Because trust is currency. According to TRM Labs' 2025 industry survey, 78% of institutional investors now require crypto platforms to demonstrate comprehensive compliance programs before engaging. This shift has accelerated since the SEC approved the first spot Bitcoin ETFs, setting a new standard for transparency. If you want access to traditional banking rails or partnerships with Fortune 500 companies, your compliance posture must be impeccable. The Financial Stability Oversight Council even identified inadequate compliance as the second highest risk factor for crypto-related financial instability. By treating compliance as a competitive advantage rather than a burden, you position your company for long-term stability and growth in an increasingly regulated market.
Frequently Asked Questions
What is the Crypto Travel Rule?
The Crypto Travel Rule is a requirement under the Bank Secrecy Act that mandates Virtual Asset Service Providers (VASPs) to share originator and beneficiary information when transferring value above a certain threshold, currently $3,000 in the US. It mirrors the existing travel rule for wire transfers to help track illicit flows.
How much does it cost to become compliant?
Costs vary widely based on size and jurisdiction. Mid-sized exchanges typically spend $50,000 to $500,000 annually on software and services. Initial implementation costs, including legal and consulting fees, can range from $100,000 to over $500,000 depending on complexity.
Is MiCA applicable to US companies?
MiCA is primarily an EU regulation. However, any US company offering services directly to EU customers may need to comply with MiCA to operate legally in that market. It creates a single passport for EU operations but does not replace US federal or state laws.
How long does it take to implement a compliance program?
For most mid-sized firms, the process takes 6 to 9 months. Larger institutions with complex legacy systems may require 12 to 18 months. The timeline depends heavily on how well your current infrastructure integrates with new compliance APIs.
What skills are needed for a crypto compliance team?
You need a hybrid skill set. Professionals must understand traditional AML/KYC regulations but also have technical knowledge of blockchain analytics, smart contracts, and wallet architectures. Finding people with both backgrounds is difficult, so many firms opt for specialized external consultants initially.
manish jha
August 21, 2026 AT 20:07Let us be honest here. Most of these 'compliance programs' are just expensive theater for the uninitiated. The real issue is that you are trying to force a decentralized protocol into a centralized box.
The EU with MiCA is fine, sure, but look at the US. It is a mess. A chaotic, beautiful mess. But calling it a 'patchwork' is an insult to the complexity. It is a labyrinth designed by lawyers who have never touched a private key in their lives. You think a $50k budget covers this? Please.
Gary Straiton
August 21, 2026 AT 20:19Oh, how quaint! You Indians always love to lecture on global affairs while your own regulatory bodies are still figuring out what a blockchain is. 🇺🇸
In America, we don't need 'guides.' We have the strongest legal system on Earth. If you can't handle 47 state licenses, maybe you shouldn't be operating in the land of the free. The cost isn't high; it's the price of doing business in a nation that actually values property rights and rule of law. Europe is just a bureaucratic swamp waiting to sink. Don't let them fool you with their 'unified path.'
alex fordy
August 23, 2026 AT 06:55It’s interesting how we frame this. 😊 I’ve been thinking about the philosophical implications of KYC. When we verify identity, are we really securing the asset, or are we just creating a new layer of surveillance capitalism?
The article mentions 'trust is currency,' which resonates deeply with me. In a world where digital assets are intangible, trust becomes the only tangible thing left. However, if the compliance stack is opaque, does it truly build trust, or just compliance fatigue? I find myself wondering if the 98% accuracy rate mentioned is a double-edged sword. Precision without context can lead to its own kind of injustice. What do you all think about the human element in all this automation?
Nia Franklin
August 23, 2026 AT 08:48OMG!! Did anyone else catch the part about the 12% stat?? That is so crazy!!! I feel like everyone is missing the boat here because they are too focused on the tech!!
I mean... seriously?! Only 12% of people know what they are doing?? It makes my head spin!! I was reading this on my commute and almost dropped my coffee!! The idea that you need people who understand BOTH finance AND code is just... wow. It’s like looking for a unicorn with a PhD in accounting!! Who even hires those people?? I bet they charge an arm and a leg!! Also, the typo in my last sentence wasn’t intentional, promise!! Just typing fast!! 😂
Sonia Gomez Gomez
August 25, 2026 AT 01:07:) Let me tell you something nobody wants to hear. You are all lazy. Yes, you. The ones complaining about the cost. You are choosing to be non-compliant because you are cheap and greedy. It is a moral failing.
If you run an exchange, you have a duty to protect the little guy from scammers. But instead, you hide behind 'friction' and 'user experience.' User experience? For whom? The money launderers? The terrorists? Stop making excuses. Pay the consultants. Hire the staff. Do the work. It is not hard. It is just uncomfortable for people who want to cheat the system. Face the music. :)
SHIV SHANKAR KANTA
August 25, 2026 AT 13:44They say compliance is a burden but I see it as a spiritual journey of purification
the blockchain is pure light yet regulators want to shackle it with chains of paper
is it not ironic that we seek freedom in code but submit to the tyranny of the state ledger
my heart aches for the true believers who are forced to wear masks of legality
we must rise above this noise and find the inner peace of the hash function
do not let them break your spirit with their forms and filings
the universe knows the truth even if FinCEN does not
keep your wallets secure and your souls more secure
this is the path of the enlightened trader
everything else is illusion
Daniel Brown
August 26, 2026 AT 04:49Just a quick note to add some perspective here, since I've been auditing VASPs for the last decade. The article glosses over the operational risk associated with API dependencies. If Sumsub or Onfido goes down, your entire KYC pipeline stalls.
We recently had a client lose three days of onboarding due to a third-party vendor outage. The 'risk-based approach' mentioned in the post assumes continuous data flow, which is a dangerous assumption in a distributed system. You need redundant identity providers. It adds cost, yes, but downtime costs more in lost revenue and user churn. Don't sleep on this one.
Marco Maldonado
August 27, 2026 AT 11:35Ugh another guide written by people who have never actually launched an exchange lol
Here is the real talk: the biggest cost isn't the software, it's the legal fees to figure out if you're allowed to exist in Delaware vs Wyoming. The article says 6-9 months? Give me a break. My team spent 14 months just getting the initial charter approved. And don't get me started on the 'Travel Rule'. It's a nightmare to implement correctly. Most companies just ignore it until they get fined. Wake up folks, the regulations are moving faster than you can read them.
Darren Moon
August 27, 2026 AT 15:04One observes with a certain degree of scepticism the prevailing narrative surrounding the efficacy of automated transaction monitoring systems. While the cited 98% accuracy rate appears impressive on the surface, one must consider the underlying false positive rates in heterogeneous blockchain environments.
The integration of AI-driven analytics often results in a significant increase in alert volume, thereby necessitating a proportional expansion of the manual review team. This creates a paradoxical situation wherein technological advancement leads to increased labour dependency. Furthermore, the interoperability challenges between disparate VASP ledgers remain largely unresolved, rendering the 'seamless backend integration' described in the text somewhat optimistic. One wonders if the industry has truly matured or merely shifted its inefficiencies to a different layer of the stack.
Quang Thai Tran
August 28, 2026 AT 15:38It is quite evident that the regulatory landscape is being manipulated by a select few banking interests seeking to maintain their monopoly. The 'MiCA' regulation is simply a Trojan horse for central bank digital currencies (CBDCs).
Notice how every major regulator pushes for 'travel rule' compliance? They are building the database for total financial surveillance. The 5-year record retention period is a drop in the bucket; they will extend it indefinitely once the infrastructure is in place. Do not be fooled by the 'competitive advantage' rhetoric. Compliance is the leash. The moment you plug in, you are no longer free. The smart money knows this and moves offshore. The rest of us are just pawns in this grand game.
Dianne Ritter
August 29, 2026 AT 15:50I think there's a lot of valid points here, but also a lot of fear-mongering. It depends on your specific use case. If you're a small DEX, you might not need the full enterprise suite immediately. But if you're aiming for institutional capital, yeah, you have to play the game. It's a balance. I guess.
Kate Staab
August 31, 2026 AT 04:26Dramatically speaking, this article is a disaster! How dare they suggest that compliance is 'optional checkboxes'? It is mandatory! It is law!
And the cost figures? Ridiculous. Why should small businesses pay the same percentage as giants? It's unfair! The EU is doing it right, obviously, because they care about order. The US is a chaos of self-interest. We need stricter rules, not guides. Guides are for people who don't know the answer. We need mandates! Full stop!
Calliope Clio
August 31, 2026 AT 08:17😒 Another generic listicle pretending to be deep insight. Really?
'You don't have to build everything from scratch.' Obviously. Who said we did? The real issue is the vendor lock-in. Once you sign with a big-name provider, you're stuck. The switching costs are astronomical. This article conveniently ignores the exit strategy. It's like buying a house without checking the foundation. Pretty paint, nice view, but structurally unsound. Yawn. #CryptoCompliance #Overrated
Abigail Sparks
September 2, 2026 AT 02:20LISTEN UP! You need to stop overthinking this! 💥
Here is the deal: Pick one jurisdiction. Get licensed. Done. Don't try to be everywhere at once. The US market is tough, yes, but the rewards are massive. If you're scared of the 47 states, start with Delaware and expand. Stop letting the fear of paperwork paralyze you. Action beats analysis paralysis every single time. Get your KYC sorted, get your AML done, and LAUNCH. The market doesn't wait for perfection. It waits for presence. Go get it! 🔥
Kelsey Anne
September 2, 2026 AT 17:16You are wrong. The timeline is shorter. The tools are better. Read the documentation. Stop guessing. Compliance is simple if you follow the rules. Do not make it complicated. It is not rocket science. It is arithmetic. Count your transactions. Check your users. File your reports. That is all. The rest is noise. Focus on the basics. The rest will follow. Trust the process. Not the hype.
Leah Humphrey
September 3, 2026 AT 03:34Leveraging Sybil attack vectors in the KYC pipeline remains a critical vector for adversarial actors, particularly when relying on biometric matching via third-party APIs. The correlation between false negative rates and subsequent AML exposure is non-linear, suggesting that a tiered risk assessment model may introduce blind spots in high-velocity transaction environments. Furthermore, the interoperability standards for Travel Rule data packets lack sufficient granularity for cross-chain bridging scenarios, potentially leading to metadata loss during multi-hop transfers. One must question whether the current consensus on 'enhanced due diligence' thresholds adequately accounts for the liquidity fragmentation observed in DeFi protocols integrated with CeFi interfaces. The empirical data presented herein suggests a need for dynamic threshold adjustment rather than static monetary caps.